
CrowdStrike and CLEAR have integrated CLEAR1 person-verification technology with the CrowdStrike Falcon platform, giving security teams a way to add high-assurance identity checks to workflows that handle potentially risky activity.
The companies said the partnership connects Falcon threat detection with CLEAR1, a platform that uses biometrics, government-issued identification and verification against authoritative sources to establish confidence in a person’s identity. The stated goal is to help organizations distinguish a trusted user from an attacker using valid credentials, a recognized device or another pathway that may otherwise appear legitimate.
The integration is available to existing CrowdStrike and CLEAR1 customers. It is designed to work with Falcon capabilities including Falcon Next-Gen SIEM and Charlotte Agentic SOAR, allowing person-based verification to be incorporated into existing security workflows rather than deployed as a separate manual process.
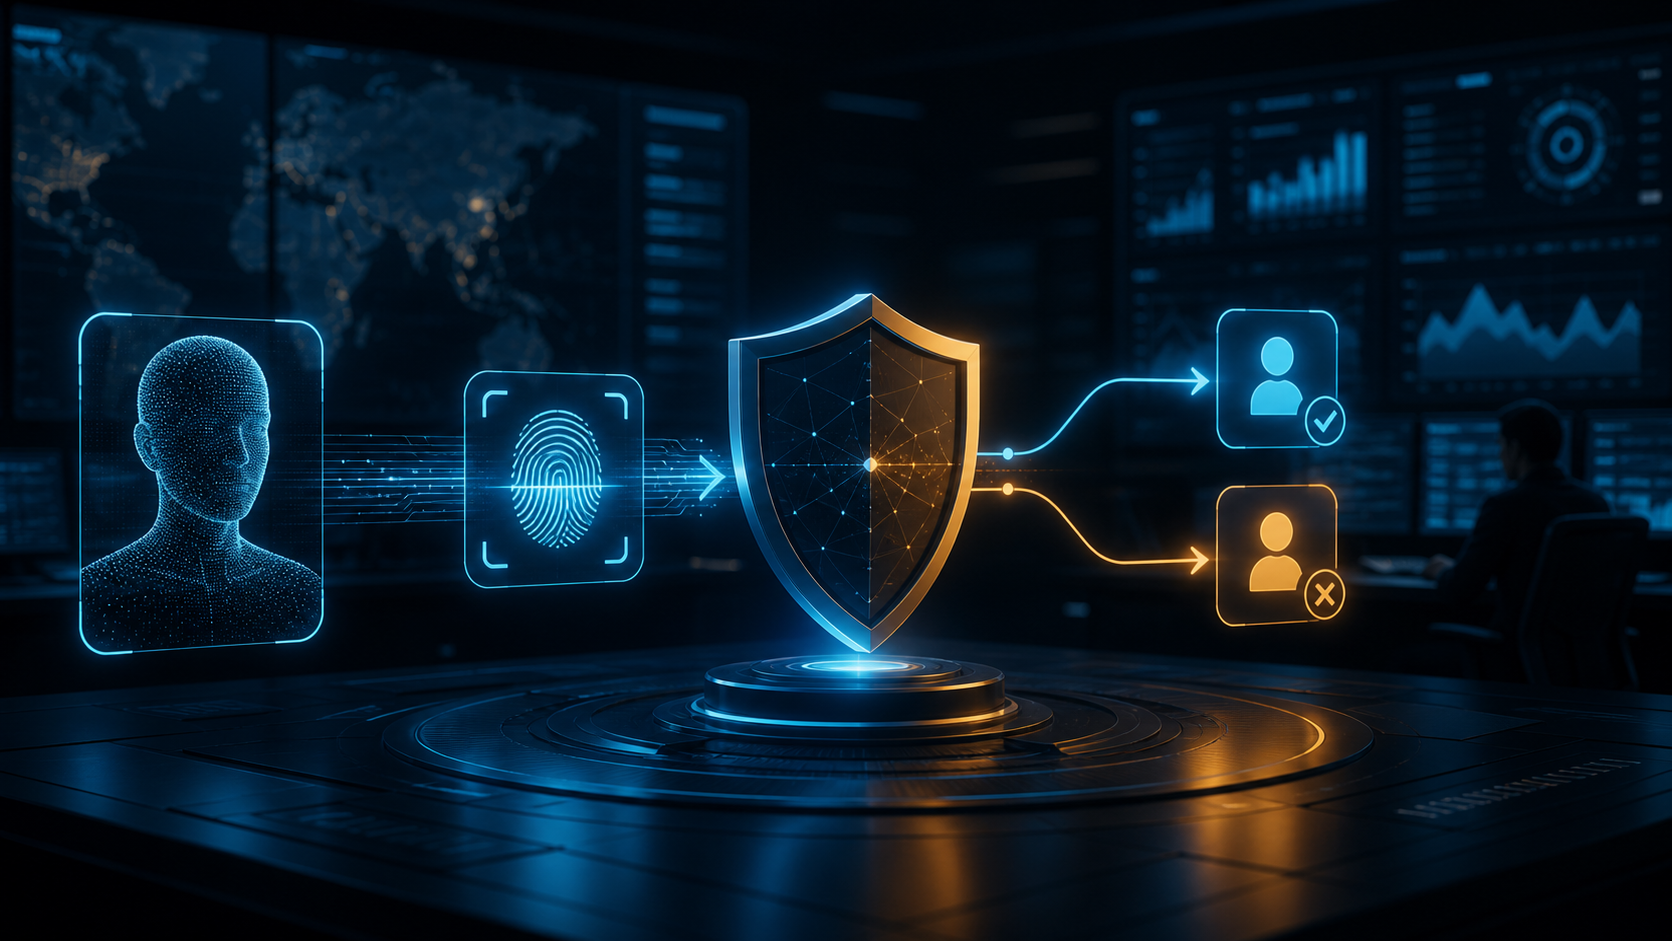
In the flow described by the companies, Falcon detects activity that could indicate risk and triggers CLEAR1 to verify the human associated with it in real time. The verification result can then be considered with other security signals to inform whether activity should be allowed, investigated or blocked.
That sequence is notable because identity-based attacks often do not look like conventional malware events. An attacker with an employee’s password, session token or approved device may generate activity resembling ordinary access. Security tools can assess device telemetry, user behavior and threat intelligence, but may still have limited information about whether the person at the keyboard is authorized to use the account.
CrowdStrike and CLEAR said the integration is intended to add that person-level signal without imposing unnecessary friction on trusted users. The release does not explain which signals would trigger a verification request, how organizations can configure thresholds, how long a verification takes or whether it reduces false positives. Those implementation details will matter for security teams deciding where to place a high-assurance check in an incident or access workflow.
Requiring verification for every unusual event would introduce overhead, while using it too selectively could leave material risks unaddressed. Each organization will need to define the events that warrant verification, the users or systems covered, and the fallback process for people who cannot complete a check. Enterprises will also need to assess how person-verification data is handled, retained and governed under their identity and access-management policies.
The automation value lies in connecting an identity decision to the operational flow that already handles detection and response. In a mature security-operations environment, a verification result could help triage an alert or determine whether an automated response should be escalated to a human analyst. It is not a replacement for core identity controls, endpoint security or incident response, but it adds a potentially useful signal when a security team needs to decide whether suspicious activity is tied to a legitimate person.
For organizations that adopt the integration, the most important design choice will be how verification outcomes are connected to policy. A positive check may support an allow decision, while an incomplete or failed check may require a review rather than an automatic block. Policies also need to account for accessibility, legitimate travel, emergency access and other cases in which the normal verification flow is unavailable.
The partnership therefore gives security teams another decision point in an automated workflow, rather than removing human judgment. Its effectiveness will depend on measured deployment, privacy review and integration with the broader controls that already govern identities, endpoints and privileged access.